

Morning meeting: From cybersecurity requirements to practical action that creates value for your business
From cybersecurity requirements to practical action that creates value for your business
Morning meeting in Odense: How do you document your cybersecurity efforts when customers, business partners and legislation impose new requirements?
For many businesses, the challenge is not a lack of ambition, but knowing where to begin, what to prioritise, and what documentation management and customers need.
D-mærket and Odense Robotics therefore invite you to two practical hours focused on moving from requirements to action that can safeguard your business value.
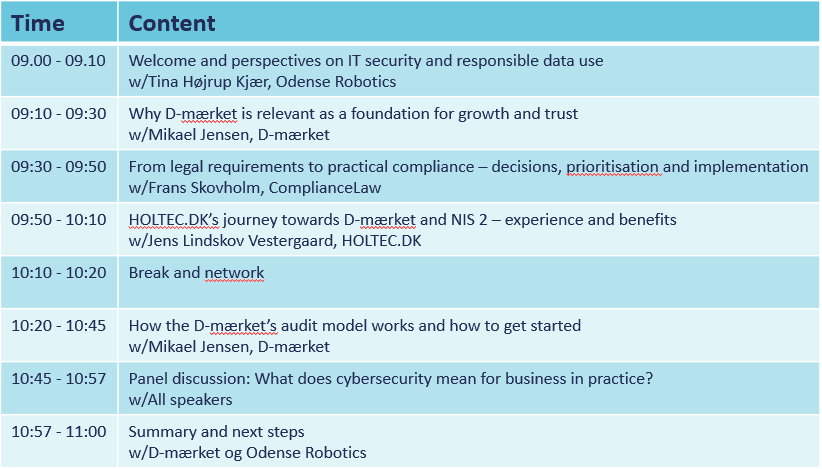
Among others, you will meet Jens Lindskov Vestergaard from HOLTEC.DK, who will share practical experience of turning requirements from cybersecurity legislation (NIS 2) into action and working towards D-mærket. You will also be introduced to D-mærket’s audit model, which can help you prioritise initiatives and develop and sustain your security efforts over time. You will also meet Frans Skovholm from ComplianceLaw, who will provide perspectives on legal requirements and practical compliance.
You will leave with:
- a clearer picture of your company’s key requirements and cybersecurity risks
- inspiration for translating legislation and customer requirements into decisions and workflows
- knowledge of how D-mærket can be used as a practical framework
- insight into how HOLTEC.DK has worked with NIS 2 and approached the process of obtaining D-mærket
- a practical next step for your company to take forward
Preparation
To get the most out of the morning meeting we recommend completing D-mærket’s Cyber Survey and bringing the report either digitally or as a printout. Participation is voluntary, and you decide what information you wish to share. The survey gives you a clear overview of your company’s cybersecurity efforts and provides recommendations for the next steps.
Register here – and take the next step towards a more resilient and credible business.
HOLTEC.DK works with industrial automation and operational technology (OT), software, control systems and complex automation solutions.
ComplianceLaw combines legal expertise with operational tools, translating legal requirements into policies, routines and business processes tailored to each company’s risk profile.
D-mærket is Denmark’s labelling scheme for IT security and responsible data use. It helps you assure consumers, customers and partners that they and their data are in safe hands with your company.
